Breachsense: Dark Web and Breach Monitoring
breachsense.com · checked 30 Sept 2026
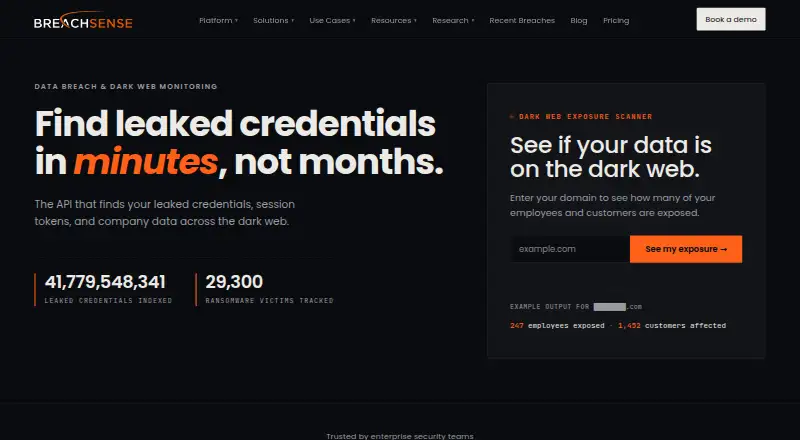
Dark web monitoring for exposed credentials, ransomware files, and lookalike domains.
How it plugs in
Signal on Dark Web Monitoring Services5.6#6 of 25
Founded in 2018, Breachsense is a paid web-and-API service that watches dark web and breach sources for organizational data. It finds exposed credentials, tokens, leaked files, and phishing domains, then sends alerts or data through an API. A seven-day full-platform trial follows a demo call, and a free dark web scan is available.
Review
In a line
For an organization, Breachsense searches dark web sources for exposed credentials, session tokens, leaked files, and related information. Access comes through its website or API.
What it does
Its searches cover credentials from breaches, infostealer logs, combo lists, exposed databases, criminal forums, marketplaces, paste sites, Telegram, IRC, and phishing-kit infrastructure. Findings may include usernames, passwords, email addresses, authentication cookies, API keys, OAuth tokens, service-account secrets, leaked files, and exposed personal data.
Full-text searches can look through ransomware leak files for company names, employee names, or other terms. The service follows victim announcements from over 100 ransomware groups and searches their published files.
Monitoring also covers subdomains, lookalike and typosquatted domains, homoglyphs, alternate top-level domains, forgotten subdomains, and Certificate Transparency logs. Domain takedown services are available.
When new credentials or session tokens appear, Breachsense can send an HTML email or JSON webhook. Those notifications can feed workflows that initiate password resets or session-token revocation through security orchestration or identity tools.
How it connects
Breachsense offers webhooks and a REST API for software integrations. JSON responses support historical queries by domain, email, username, IP address, or keyword and include breach source, date, and exposed-data details.
SIEM, SOAR, ticketing, chat, and other systems accepting these interfaces can connect through the webhooks or API. MSP plans add per-client webhook routing for monitoring multiple customers.
According to the company, data is encrypted in transit and at rest, access is restricted to employees who need it, and customer data is not sold. Breachsense states compliance with GDPR and CCPA.
Good fit
The stated customer groups are enterprise security teams, managed security service providers, security consultants, penetration testers, and red teams.
It suits organizations that need credential and ransomware-leak searches, attack-surface monitoring, alert automation, or API access to historical results. Personal and business monitoring are supported.
Watch for
Code repositories, social media profiles, endpoints, and network traffic are outside Breachsense's monitoring. Check that its dark web and breach coverage matches the data sources you need.
Plan pricing varies with watchlist size, API query quota, alert latency, premium dark web market coverage, and included domain takedowns.
Pricing
Breachsense has four paid pricing tiers, with prices available on request; it has no free plan.
A free dark web scan is available, and a demo call precedes seven days of full-platform access. All plans include compromised credential detection, ransomware leak file search, webhook and email alerts, and API access.
Verdict
Choose Breachsense when security work focuses on dark web exposure, ransomware disclosures, lookalike domains, and automated response through webhooks or an API. MSP-specific routing may help teams watching several clients.
It is not a match for teams seeking repository, endpoint, social-media, or network-traffic monitoring. Buyers should request pricing and confirm coverage, alert timing, API limits, and domain-takedown needs before committing.
Our take
Breachsense fits security groups that need one place to find exposed credentials, tokens, ransomware files, and impersonating domains. Its email alerts, webhooks, and JSON API can feed existing response tools, while MSP routing supports multi-client work. The service is paid, with pricing on request and no free plan, although a scan and a short trial are available. Avoid it if you need endpoint, repository, social-media, or network monitoring. Ask about the four pricing factors and confirm that the available sources cover your organization.
- Searches credentials, tokens, leaked files, and exposed personal data
- Follows ransomware announcements from over 100 groups
- REST API and webhooks support security-tool connections
- Monitors lookalike domains and offers domain takedowns
- MSP plans include per-client webhook routing
- No free plan; paid pricing is available only on request
- Does not monitor endpoints, repositories, social profiles, or network traffic
- Full-platform trial requires a demo call
- Alert timing and coverage vary by pricing tier
- Pick it ifEnterprise security and managed security service teams; Penetration testers and red teams; Organizations needing API-driven dark web alerts
- Skip it ifYou need endpoint, code-repository, social-media, or network monitoring; You require published prices or a permanent free plan
Pricing
Four paid tiers are priced on request. Tier differences include watchlist size, API query quota, alert latency, premium dark web market coverage, and included domain takedowns. A free dark web scan and a seven-day full-platform trial after a demo call are available.
- Four pricing tierswatchlist size · API query quota · alert latency · premium dark web market coverage · included domain takedownsOn request
As breachsense.com lists them, checked 30 Sept 2026.
Questions
Does Breachsense have a free plan?
No. Breachsense is paid, though it provides a free dark web scan and seven days of full-platform access after a demo call.
What can Breachsense search for?
Queries can use a domain, email, username, IP address, or keyword, with results showing breach source, date, and exposed-data details.
Can it monitor ransomware leaks?
Yes. Full-text searches cover leaked ransomware files, while victim announcements from over 100 ransomware groups are tracked.
How are alerts delivered?
Newly detected credential or session-token exposure can arrive by HTML email or JSON webhook.
Does Breachsense have an API?
Yes. The REST API returns JSON and supports historical queries using a domain, email, username, IP address, or keyword.
What does Breachsense not monitor?
Monitoring excludes code repositories, social media profiles, endpoints, and network traffic.
Who is Breachsense for?
Its identified customers include enterprise security teams, managed security service providers, security consultants, penetration testers, and red teams.
Near it
All alternatives →- D
 DARKX#5 on this board
- DD
 Deepinfo Dark Web Monitoring#7 on this board
- JD
 Jsmon Dark Web Monitoring#4 on this board
- PPassguard#8 on this board
- EeMonitor#3 on this board
- D
 DarkThreat#9 on this board
- PPhishEye#2 on this board
- DV
 DarkOwl Vision UI#10 on this board
- CD
 CyberGuard360 Deep Diver#1 on this board
- FFlare#11 on this board