Check Point DDoS Protector
checkpoint.com · checked 4 Oct 2026
Real-time DDoS mitigation for enterprise networks and service providers.
How it plugs in
Signal on DDoS Protection Software5.3#10 of 37
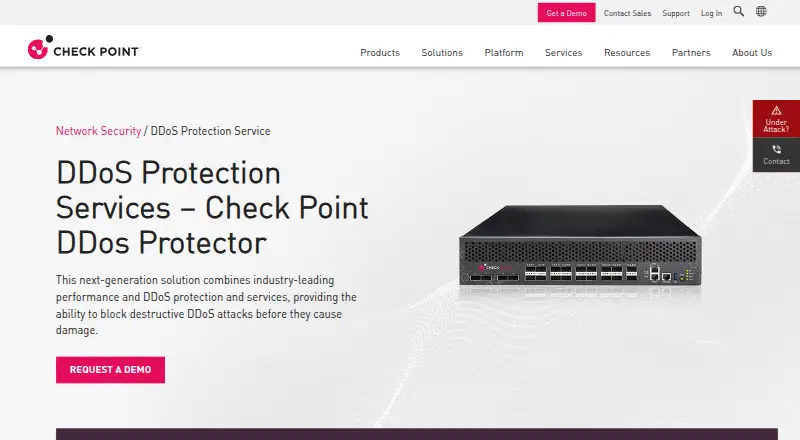
Check Point DDoS Protector is a perimeter device that mitigates attacks against networks and applications. Behavioral AI and machine learning generate signatures in real time for threats including DNS amplification, IoT botnet floods, SSL/TLS floods, and attacks spanning Layers 3–7. Deployment choices include inline, monitoring, out-of-path, cloud, hardware, hybrid, and virtual forms.
Review
In a line
Check Point DDoS Protector provides real-time distributed-denial-of-service mitigation for network and application environments. Its documented users include enterprise networks, cybersecurity operations, and service providers.
What it does
Behavioral AI and machine-learning methods automatically address both established and zero-day attack patterns. Coverage includes DNS amplification, IoT botnet floods, SSL/TLS floods, and threats affecting network Layers 3 through 7.
Attack signatures are generated as events occur, with detection and protection stated at under 10 seconds. Depending on the model, programmable mitigation capacity can reach 800 Gbps, while listed latency is below 60 microseconds.
A dashboard presents detection events, policy controls, and configuration tools. Check Point’s Emergency Response Team can set up, operate, and tune on-premises devices.
How it connects
Traffic can pass inline, be observed through a SPAN or copy port, or be mitigated out of path. Check Point describes cloud, hardware, hybrid, and virtual-appliance formats for software-defined data centers.
The X Series connects with Check Point’s Hybrid Cloud DDoS Protection Service as part of a unified hybrid arrangement. Other listed capabilities include API access, policy automation, threat intelligence, encrypted-traffic and SSL inspection, intrusion prevention, and site-to-site VPN support.
It runs in self-hosted and Linux environments, with cloud support also listed. For related tools, see DDoS protection software and network firewall software.
Good fit
Organizations seeking defense for network and application traffic can use its inline blocking and varied deployment modes. Multitenant and multipolicy operation is also documented for service providers.
It fits teams that want centralized visibility, automated policy handling, and optional managed mitigation. A virtual appliance can serve software-defined data centers, while cloud and hybrid options cover cloud workloads.
Watch for
Select the model and traffic arrangement with care because inline, monitoring-port, and out-of-path configurations serve distinct network functions. Model choice also determines the maximum programmable mitigation rate, which is listed as high as 800 Gbps.
The support materials specify one year of hardware and software maintenance. Confirm the level of continuing support and tuning needed, including whether Check Point’s Emergency Response Team should operate the device.
Pricing
Check Point describes DDoS Protector as a paid hardware and software product with pricing provided on request. A free Quantum DDoS Protector demo is available through a request form.
Verdict
Consider it when your organization needs DDoS response stated at under 10 seconds, broad attack-layer coverage, and hardware, cloud, hybrid, or virtual choices. Service providers can use its multitenant and multipolicy capabilities.
Look elsewhere if you need a publicly posted price or a simple consumer-focused product. Buyers should first confirm the right model, deployment path, throughput, and support terms with Check Point.
Our take
Check Point DDoS Protector targets organizations defending important network and application services. It addresses common flood types and Layers 3–7, with automated signatures intended to act in under 10 seconds. Larger teams can choose among cloud, hardware, hybrid, and virtual formats, while service providers have multitenant and multipolicy support. Pricing is supplied on request, and a free demo is available for evaluation.
- Protection includes DNS, IoT botnet, SSL/TLS, and Layers 3–7 threats
- Real-time signatures can detect and protect in under 10 seconds
- Deployment formats span cloud, hardware, hybrid, and virtual options
- API connectivity, policy automation, and managed mitigation are available
- Programmable capacity can reach 800 Gbps, model depending
- A quote is required for pricing
- Throughput differs across models
- The listed hardware and software maintenance term is one year
- Pick it ifEnterprise networks requiring broad DDoS coverage; Service providers that need multitenant and multipolicy controls; Teams considering cloud, hardware, or hybrid deployment
- Skip it ifYou require a published price before vendor contact; You want a basic product for small, single-site use
Pricing
This paid product is priced on request, so buyers must contact Check Point for a quote.
Questions
Which attack types are covered?
Coverage includes DNS amplification, IoT botnet floods, SSL/TLS floods, and attacks affecting network and application Layers 3 through 7.
What response time does it specify?
Check Point states that real-time signatures can identify attacks and provide protection in less than 10 seconds.
How can the device be deployed?
Supported arrangements include inline operation, SPAN-port or copy-port monitoring, and out-of-path mitigation; cloud, hardware, hybrid, and virtual-appliance formats are also described.
Can it protect cloud environments?
Yes. Cloud workload support is listed, and the X Series connects with Check Point’s Hybrid Cloud DDoS Protection Service.
Where can I get pricing information?
Pricing is provided on request. Check Point also offers a free demo through a request form.
Near it
All alternatives →- AWAndrisoft Wanguard#9 on this board
- SAStormWall Appliance#11 on this board
- SDStormWall DDoS Protection#8 on this board
- CCCisco Catalyst Center#12 on this board
- AS
 AWS Shield#7 on this board
- PNPath Network DDoS Protection#13 on this board
- HHaltdos#6 on this board
- CA
 Cloudflare Advanced Certificate Manager#14 on this board
- PSProject Shield#5 on this board
- QD
 Qrator DDoS Protection#15 on this board