Endor Labs: Code, Dependency, and AI Security
endorlabs.com · checked 21 Oct 2026
Endor Labs helps teams assess software code, dependencies, secrets, containers, and AI-generated software.
How it plugs in
Signal on Secrets Scanning Software6.7#1 of 24
Endor Labs analyzes code and open-source dependencies for security issues, exposed secrets, and risky packages. It also scans container images and supports governance for coding agents and AI models. Scanning is available locally, in CI runners, and through cloud apps; eligible customers can use an on-premises deployment. The Developer tier is free, while paid plan prices are available on request.
Review
In a line
Endor Labs analyzes application code, dependencies, secrets, containers, and AI-generated software to identify security risks.
What it does
Endor Labs checks an application’s own code and the open-source packages it uses. Its code scanning looks for flaws and exposed credentials, while its dependency analysis links vulnerabilities to the functions an application can actually reach.
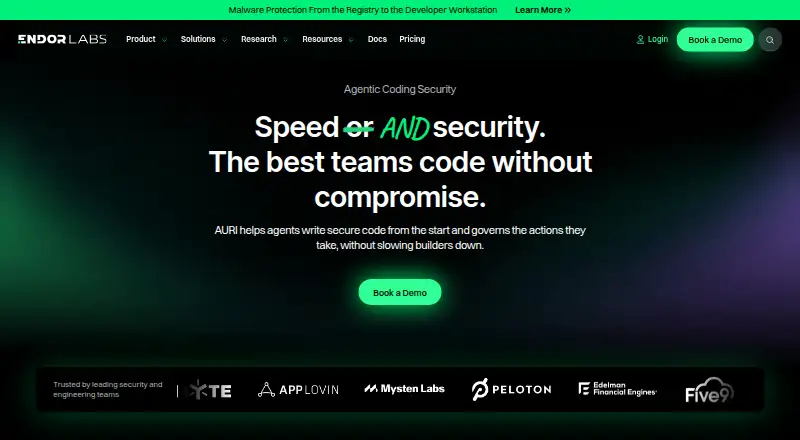
Container image analysis connects vulnerabilities to application reachability. Package Firewall is designed to stop vulnerable or malicious packages before installation, and upgrade impact analysis identifies likely breaking changes when a direct dependency is updated. For AI coding workflows, AURI helps scan and fix vulnerabilities, detect secrets, and block malicious dependencies. The platform can inventory coding agents, AI models, MCP servers, and skills, and enforce policies on agent actions.
How it connects
Listed integrations include GitHub, GitLab, Bitbucket, CircleCI, Jenkins, Jira, and Slack, along with Vanta and coding tools such as Cursor, Claude, Gemini, and GitHub Copilot. An MCP server connects security checks to coding assistants and IDEs, including Gemini CLI, Claude Code, Cursor, Codex, and VS Code.
Available scanning routes include cloud apps and CI runners. Endor Outpost offers scheduled monitoring and on-premises deployment for eligible customers. The Developer tier scans locally; paid plans include a web interface and REST API. The public Endor Labs Agent Kit is licensed under MIT.
For cloud scans, Endor Labs says source is briefly cloned into a scanning container, which is destroyed after the scan. CI scans can leave code in the customer's runner.
Good fit
Endor Labs may suit software teams that need to check their own code alongside open-source dependencies, including in pull requests. Its documented SCA language list includes C#, Go, Java, JavaScript and TypeScript, Kotlin, PHP, Python, Ruby, Rust, Scala, and Swift.
It may also fit teams that need container scanning, software bill of materials (SBOM) records, or controls for AI coding agents. Package scores draw on security, quality, popularity, and activity signals.
Watch for
The free Developer tier is for local scans and read-only vulnerability data; it does not include a web interface, policies, or scan history.
Endor Outpost is available to eligible customers, not described as a general self-hosting option. Documentation gives minimum and recommended runner resources and notes that large applications may require more capacity.
Pricing
The Developer plan is free, with local scanning and read-only access to vulnerability data; it has no web interface, policies, or scan history.
Core and Pro prices are available on request. Paid plans have annual fair-use quotas tied to purchased seats, but scanning is not blocked when those limits are exceeded. A free trial is available.
Verdict
Consider Endor Labs if your team wants a shared way to review code, dependencies, secrets, containers, and AI coding workflows, and its integrations and deployment options fit your setup. The free tier allows limited local scanning but lacks a UI and several team features. For policies, deeper scanning, or reporting, ask about paid-plan terms and annual seat-based quotas. Teams that do not need application security scanning are unlikely to need this platform.
Our take
Endor Labs may be a fit for teams assessing code and open-source dependencies together, or seeking controls for coding agents and AI models. Its integrations and deployment options support different workflows. The free tier covers local scans and read-only vulnerability data, without a web interface, policies, or scan history. Because paid prices are available on request, ask for plan details and confirm deployment eligibility before choosing it.
- Checks code, dependencies, exposed secrets, and container images.
- Maps dependency vulnerabilities to reachable code paths.
- Lists integrations with common code, build, issue, and chat tools.
- Offers a free local-scanning tier and a free trial.
- Supports cloud and CI scanning, with on-premises deployment for eligible customers.
- The free tier has no web interface, policies, or scan history.
- Core and Pro prices are available only on request.
- On-premises Endor Outpost is for eligible customers.
- Large applications may need additional runner resources.
- Pick it ifTeams assessing code and open-source dependencies together; Organizations governing AI coding agents and models; Teams needing CI, cloud, or eligible on-premises scans
- Skip it ifYou need a free tier with a web interface, policies, or scan history; You need published prices before contacting a vendor; You do not need application-security scanning
Pricing
The free Developer tier offers local scanning and read-only vulnerability data. Core and Pro prices are available on request; paid plans use annual seat-based fair-use quotas, and scans are not blocked when a quota is exceeded.
- DeveloperFREE · AURI scanning locally · read-only vulnerability data · no UI, policies, or scan historyFree
- CoreGet started · Reachability · prioritization · policies · deeper scanning and enterprise integrationsOn request
- ProGet started · Advanced detection, triage, and remediation across application layers · reporting and workflow featuresOn request
As endorlabs.com lists them, checked 21 Oct 2026.
Questions
Is Endor Labs free?
Yes. The free Developer plan includes local scanning and read-only vulnerability data, without a web interface, policies, or scan history.
How much do Core and Pro cost?
Both are priced on request. Paid plans use annual fair-use quotas based on purchased seats, but scanning is not blocked when a quota is exceeded.
Which tools does Endor Labs integrate with?
Listed integrations include GitHub, GitLab, Bitbucket, CircleCI, Jenkins, Jira, Slack, Vanta, Cursor, Claude, Gemini, and GitHub Copilot.
Can Endor Labs scan inside our own environment?
Teams can run scans in CI runners. Endor Outpost offers on-premises deployment for eligible customers.
Does Endor Labs keep source code from cloud scans?
Endor Labs says cloud scans briefly clone source into a scanning container and destroy it afterward. CI scans can retain code in the customer's runner.
Does Endor Labs support AI coding tools?
Its MCP server connects security checks to tools such as Gemini CLI, Claude Code, Cursor, Codex, and VS Code. AURI supports security checks in AI coding workflows.