Checkmarx API Security: What to Know
checkmarx.com · checked 21 Oct 2026
Checkmarx API Security finds APIs and security risks in source code and API documentation.
How it plugs in
Signal on API Security Software5.6#11 of 30
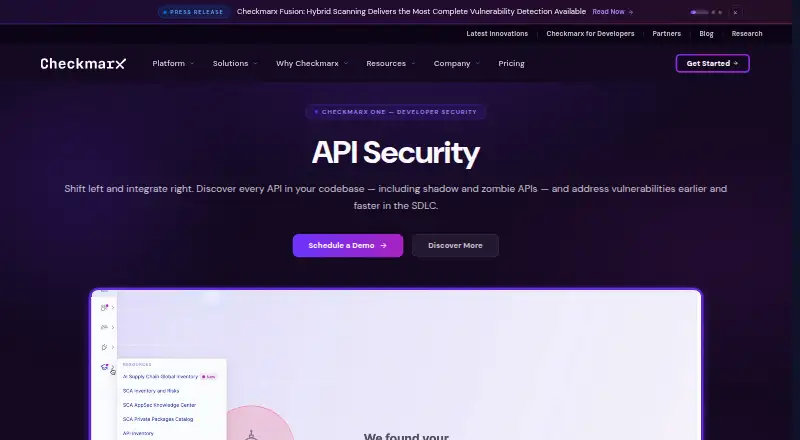
Checkmarx API Security builds an inventory of APIs found in application code and documentation, including undocumented or abandoned endpoints. It tracks changes, flags vulnerabilities, and can correlate API risks with Checkmarx runtime testing. It connects with common code repositories, build tools, and developer editors. Quotes are provided on request, and there is no free plan or self-serve trial.
Review
In a line
Checkmarx API Security finds APIs in application code and documentation, then records detected vulnerabilities in an API inventory. It is part of Checkmarx One.
What it does
The scanner can find undocumented APIs and endpoints that are no longer in use. It also checks OpenAPI, Swagger, and Postman documentation against the inventory to spot gaps or mismatches.
Teams can use the inventory to prioritize fixes by business risk. The API Change Log shows endpoint history, including the commit and developer linked to a change that introduced a vulnerability. Checkmarx DAST findings can be linked with SAST findings in the unified inventory, showing which issues were confirmed during runtime testing.
How it connects
Repository connections include GitHub, GitLab, Bitbucket, and Azure DevOps. Scans can run when code is pushed or a pull request is opened, including for self-hosted repositories. The documented tool integrations span Jenkins, GitHub Actions, TeamCity, VS Code, Visual Studio, JetBrains, and Eclipse.
Checkmarx One also provides REST APIs for projects, scans, results, vulnerability management, and webhooks, plus a command-line tool for project and scan management. The documented framework support includes Java Spring, ASP.NET Web API, Python Flask and Django, and Node.js Express.
Good fit
Application security teams may find this useful when they need an API inventory, visibility into undocumented endpoints, and links between API risks, code changes, and runtime test results. It may also fit teams already using Checkmarx One and its repository or development-tool connections.
Watch for
Check the supported framework list against your applications before choosing it. Its scanner's listed targets are source code and API documentation; runtime findings are correlated through Checkmarx DAST.
A free plan and self-serve trial are not available. Checkmarx directs prospects to a personalized demo. Deployment, developer count, and modules affect the custom quote.
Pricing
Pricing is on request. Checkmarx bases custom quotes on the selected modules, deployment model, and number of developers in scope. Its listed bundles also refer to developers, apps, and usage.
The Essentials bundle lists SAST, SCA, API Security, and ASPM. Professional adds malicious package protection, repository health, DAST, and container security; Enterprise adds IaC Security, secrets detection, and Codebashing. A personalized demo is available instead of a self-serve trial.
Verdict
Teams looking to discover APIs in source code and documentation, trace changes that introduce risk, and connect API findings with Checkmarx runtime testing may want to consider it. Its repository, build, and editor connections may also suit teams working within those tools.
Look elsewhere if you need a free way to start, or if your applications rely on frameworks outside the documented support list. Ask Checkmarx for a quote based on your deployment and team scope before deciding.
Our take
Checkmarx API Security is worth considering for teams that need a current inventory of APIs, including endpoints that are undocumented or no longer used. Its change history and links between source-code findings and runtime testing can help security teams investigate and prioritize risks. The main decision points are framework coverage, fit with your current tools, and a custom quote. Buyers seeking a free plan or self-serve trial should look elsewhere.
- Finds undocumented and abandoned API endpoints.
- Compares API documentation with the API inventory.
- Tracks endpoint history, commits, and developers.
- Correlates API risks with Checkmarx DAST findings.
- Connects with major repositories and development tools.
- A free plan and self-serve trial are unavailable.
- Pricing is custom quoted.
- Framework support should be checked against your applications.
- Pick it ifTeams that need an inventory of APIs found in code and documentation; Teams tracing API risks to code changes and runtime testing
- Skip it ifA free plan or self-serve trial is required.; Your apps use frameworks outside the documented support list.
Pricing
Every listed plan uses request-based pricing. Quotes vary by modules, deployment, developer count, apps, and usage. Checkmarx provides a personalized demo rather than a self-serve trial.
- Checkmarx One bundlePricing is based on developers, apps, and usage. · Custom quote · Pricing based on developers, apps and usageOn request
- EnterpriseEssentials and Professional plus IaC Security · secrets detection · CodebashingOn request
- EssentialsSAST · SCA · API Security · ASPMOn request
- ProfessionalEssentials plus malicious package protection · repository health · DAST · container securityOn request
- Start with SASTSAST · optional API Security · IaC Security · secrets detection · Checkmarx Assist · Codebashing · AI InventoryOn request
- Start with Supply ChainSCA · malicious package protection · repository health · container securityOn request
As checkmarx.com lists them, checked 20 Sept 2026.
Questions
What does Checkmarx API Security do?
It discovers APIs in source code and documentation, records detected vulnerabilities, and helps teams prioritize fixes by business risk.
Can it find undocumented APIs?
Yes. The scanner can identify undocumented endpoints and abandoned APIs, while documentation comparisons reveal discrepancies in the API inventory.
Which frameworks does it support?
Documented support includes Java Spring, ASP.NET Web API, Python Flask and Django, and Node.js Express. Check coverage for your applications before choosing it.
What tools does it connect to?
Repository connections include GitHub, GitLab, Bitbucket, and Azure DevOps. Listed plugins cover Jenkins, GitHub Actions, TeamCity, VS Code, Visual Studio, JetBrains, and Eclipse.
Does it have a free plan or trial?
No free plan or self-serve trial is available; Checkmarx offers a personalized demo instead.
How much does it cost?
Pricing is available on request. The quote reflects modules, deployment model, and developers in scope, while bundle pricing also references apps and usage.
Near it
All alternatives →- AA
 apPosture API Security#10 on this board
- TA
 ThreatX API and Application Protection#12 on this board
- HHaltdos#9 on this board
- A
 APIDynamics#13 on this board
- IA
 Imperva API Security#8 on this board
- DA
 DataDome API Protection#14 on this board
- WAWallarm API Security#7 on this board
- PA
 Palo Alto Networks Cortex Cloud API Security#15 on this board
- CPCisco Panoptica#6 on this board
- TATraceable API Security Platform#16 on this board