Imperva API Security
imperva.com · checked 15 Oct 2026
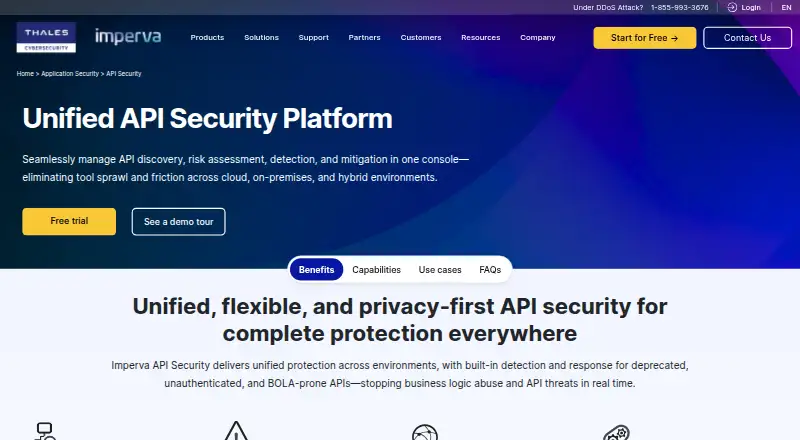
Imperva API Security unifies API discovery, assessment, testing and protection for cloud, on-premises and hybrid deployments.
How it plugs in
Signal on DDoS Protection Software5.9#4 of 37
A single console brings together API inventory, risk review, testing, threat detection and mitigation. It monitors public, private and shadow APIs, reviews OpenAPI files, detects BOLA exploits and classifies sensitive information. Cloud-managed and self-managed options cover cloud WAF, microservices, Kubernetes and network monitoring. Paid access is quote-based, and a 30-day trial is offered.
Review
In a line
Imperva API Security is a proprietary service for locating, evaluating and securing APIs. Cloud, on-premises and hybrid environments can be managed from one console.
What it does
Public, private and shadow APIs are continually inventoried and monitored; changes, design defects and vulnerabilities are tracked as they emerge. Ongoing checks address risks associated with the OWASP API Security Top 10, while API sensitivity categories include government IDs, payment-card details, addresses and other personal data.
API specification scans look for posture gaps, configuration weaknesses, risky endpoints and design flaws. API verification checks specifications and creates targeted fuzzing tests from observed behavior. OpenAPI scans can produce prioritized fixes and CI/CD notes before release.
Behavioral analysis paired with rules scores anomalies and spots business-logic abuse, such as Broken Object Level Authorization (BOLA), where access to another user’s object is gained improperly. Machine-learning profiles can identify and stop BOLA exploits as they happen. Integration with Advanced Bot Protection helps identify sensitive APIs, detect bots and apply mitigation policies.
How it connects
Imperva lists integrations with Kong, Mulesoft, Azure APIM, Apigee and F5. Management can be hosted by Imperva or operated locally, using either agent-based or agentless setups for cloud WAF, microservices, encrypted applications and network monitoring. Supported topologies include Kubernetes sensors, sidecar sniffers and standalone network sniffers.
A documented REST API uses API ID and API key headers for onboarding and configuration. Its coverage includes service and account management, policy updates, monitoring, audits, alerts, users, keys and subscription metrics. Imperva also publishes a Python SDK with JSON import and export for the SecureSphere Open API.
The core product is not open source. A separate MIT-licensed Python integration tool connects Cloud API Security with 3scale, Azure API Management, Amazon API Gateway and filesystem sources.
Good fit
This suits organizations that need one place to discover APIs, manage their security posture, detect threats and enforce protections across mixed environments. It supports runtime protection, specification governance, sensitive-data detection, rate limiting, managed rules and bot management.
It is aimed at enterprise environments, including banks, financial-services firms, telecom providers and other large companies. With Imperva’s application security platform, teams can address nine of the OWASP API Top Ten risks; Unsafe Consumption of APIs remains outside that scope.
Watch for
Check deployment and traffic requirements before purchase. The 30-day trial may be limited to 100 Mbps, and traffic above that level may be null-routed. The product is proprietary, so open-source licensing is not available.
Confirm whether your architecture fits the available cloud-managed, self-managed, agent-based or agentless choices, including WAF, Kubernetes and network-monitoring options. Also verify the OWASP coverage you need, since Unsafe Consumption of APIs is the stated exception when used with Imperva’s application security platform.
Pricing
The Free trial costs free for 30 days and includes Cloud WAF, DDoS, Bot Protection and CDN. Trial bandwidth may be limited to 100 Mbps.
The Imperva API Security plan is price on request. It is billed through contact with sales and covers enterprise API security through a Cloud WAF add-on or API Security Anywhere. There is no ongoing free plan.
Verdict
Choose Imperva API Security if you need API inventory, testing, behavior-based protection and bot controls across cloud and local systems, and can work with a paid enterprise sales process. Its REST API, Python SDK and deployment choices support operational integration.
Look elsewhere if you require open-source core software, published pricing or a permanent free tier. Before signing, confirm bandwidth limits, topology support and whether the OWASP risks important to your APIs are covered.
Our take
Imperva API Security suits larger teams seeking ongoing API inventory, risk review and runtime controls across varied infrastructure. Its testing workflow, BOLA blocking, sensitive-data classification and bot integration span several protection stages. Trade-offs include proprietary licensing, sales-led pricing and a trial bandwidth ceiling that could constrain evaluation. Buyers should confirm deployment fit and required OWASP coverage, especially if unsafe API consumption or open-source software is essential.
- Ongoing inventory of public, private and shadow APIs
- Real-time BOLA detection with blocking capability
- Cloud-hosted or locally managed deployment choices
- REST API, Python SDK and several gateway integrations
- 30-day trial includes Cloud WAF, DDoS, Bot Protection and CDN
- Pricing is available only on request
- No permanent free plan
- Core product is proprietary, not open source
- Trial traffic may be limited to 100 Mbps
- Unsafe Consumption of APIs is outside the stated OWASP scope
- Pick it ifEnterprise API teams working across cloud, on-premises and hybrid systems; Organizations needing API discovery plus runtime threat controls; Teams using gateways such as Kong, Apigee or Azure APIM
- Skip it ifYou need an open-source API security product; You require public prices or a permanent free tier; Your evaluation needs more than the trial's possible 100 Mbps limit
Pricing
A 30-day free trial is available, with possible 100 Mbps bandwidth limits. The paid Imperva API Security plan has price-on-request billing and no free tier.
- Free trial30 days · Cloud WAF, DDoS, Bot Protection and CDN included · trial bandwidth may be limited to 100 MbpsFree
- Imperva API SecurityContact sales · Enterprise API security; Cloud WAF add-on or API Security AnywhereOn request
As imperva.com lists them, checked 15 Oct 2026.
Questions
Does Imperva API Security have a free plan?
No. It offers a 30-day free trial, but no ongoing free plan.
What does the free trial include?
The trial includes Cloud WAF, DDoS, Bot Protection and CDN. Bandwidth may be limited to 100 Mbps.
Can it detect BOLA attacks?
Yes. Machine-learning behavioral profiling can detect and automatically block Broken Object Level Authorization attacks in real time.
Which API gateways integrate with it?
Imperva lists Kong, Mulesoft, Azure APIM, Apigee and F5. A separate MIT-licensed Python tool connects additional API sources.
Is Imperva API Security open source?
No. The core product is proprietary. Imperva also publishes a separate MIT-licensed Python integration tool.
Does it provide a public API?
Yes. Documented REST APIs use API ID and API key headers and cover management, policies, monitoring, audits, alerts, users, keys and subscription metrics.
Which OWASP API risks does it cover?
When paired with Imperva’s application security platform, it covers nine risks in the OWASP API Top Ten. Unsafe Consumption of APIs is excluded.
Near it
All alternatives →- GD
 Gcore DDoS Protection#3 on this board
- PSProject Shield#5 on this board
- FFastNetMon#2 on this board
- HHaltdos#6 on this board
- OC
 Oracle Cloud Infrastructure Secret Management#1 on this board
- AS
 AWS Shield#7 on this board
- SDStormWall DDoS Protection#8 on this board
- AWAndrisoft Wanguard#9 on this board
- CP
 Check Point DDoS Protector#10 on this board
- SAStormWall Appliance#11 on this board