Sumo Logic: Log Management, Security and Pricing
sumologic.com · checked 14 Oct 2026
Cloud-based log analytics, security and observability service with free access and a 30-day trial.
How it plugs in
Signal on Threat Hunting Software6.7#2 of 29
Sumo Logic collects and examines logs and metrics drawn from cloud, on-premises and hybrid environments. It offers dashboards, live monitoring, security analytics, SIEM, automated response and machine-learning root-cause analysis. Its API, Terraform provider and broad integration catalog help connect tools and automate work.
Review
In a line
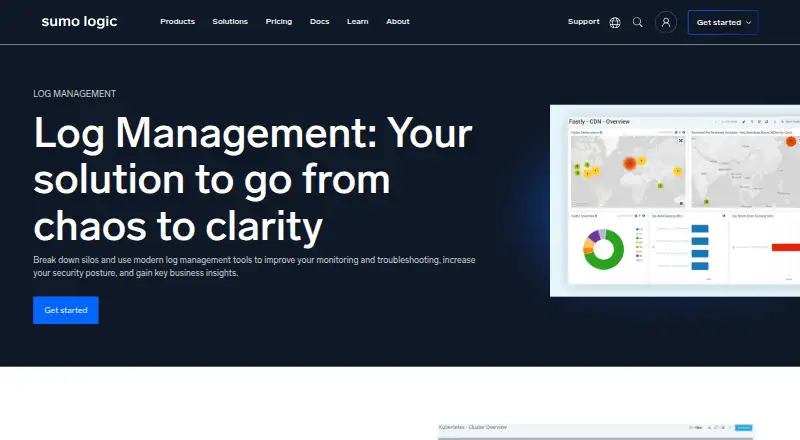
As a cloud-native SaaS offering, Sumo Logic handles log analytics, security monitoring, observability and DevSecOps. It combines logs and metrics to support monitoring, investigations and compliance work.
What it does
Its log-management tools centralize information from cloud, on-premises and hybrid environments. Users can search events, follow activity as it arrives, create dashboards and visualize data.
Security features provide centralized threat detection, indicators-of-compromise detection, threat intelligence and automated response workflows. Enterprise Suite adds a cloud SIEM with entity-centric detection, MITRE ATT&CK mapping and UEBA-driven coverage.
DojoAI offers Mobot for natural-language log analysis, a SOC Analyst Agent, a Root Cause Agent and an MCP Server that connects AI clients with Sumo context.
How it connects
The cloud service is accessible through web, Windows, macOS, Linux and API clients. AWS, Azure and Google Cloud can be connected with one click, and the catalog lists more than 150 apps and native integrations. It also lists Kubernetes, databases, SaaS products, security tools and Amazon services.
Log pipelines, structured parsing, live tailing and archive export are supported. Product APIs cover data retrieval, searches, dashboards, collectors, reports, automation and Cloud SIEM operations. A community Python REST interface and Terraform provider are available too.
The product is proprietary rather than open source, and the reviewed material does not describe a self-hosted edition. See SIEM software and SOAR software for related categories.
Good fit
Sumo Logic works for teams that need a common view of logs and metrics spanning cloud, on-premises and hybrid systems. It supports troubleshooting, security investigations, compliance activities and DevSecOps work.
Its dashboards, integrations, live analysis and API suit organizations linking numerous services or automating monitoring processes.
Watch for
The query language can require study, and reviewers describe a learning period before users get useful results. Large datasets may produce slower searches; advanced API work and support response times can also be difficult.
Usage and retention strongly affect cost. Reviewers caution that stored-log charges can climb quickly. Gartner reviewers additionally note inconsistent collection and parsing plus a need for wider vendor reporting and threat-intelligence coverage.
An installed Collector needs at least one CPU core, 512 MB of memory and 8 GB of disk. Verify supported operating systems and browser versions before deployment or access planning.
Pricing
Sumo Logic follows a freemium pricing approach. Free has no ingestion, retains data for 7 days and permits up to 3 users.
The free trial runs for 30 days, allocates 1 GB per day, retains data for 30 days and allows up to 20 users; it then converts to Free.
Essentials is quoted on request, with annual commitment referenced for example pricing. Enterprise Suite also requires a sales quote. Paid tiers add capabilities such as dashboards, anomaly detection, integrations and SIEM functions.
Verdict
Choose Sumo Logic when centralized logs, extensive cloud connections and security analysis outweigh the need for a very simple setup. Free options let small teams evaluate the service, while paid tiers extend monitoring and SIEM capabilities.
Budget time to learn the query language and manage ingestion and retention carefully. Teams requiring local deployment should look elsewhere because the product is presented as cloud SaaS without a stated self-hosted edition.
Sumo Logic serves organizations overseeing logs in multiple environments that want monitoring, security analytics and automation in one cloud service. API, integration and Terraform support connect existing systems. Main drawbacks are the learning curve, usage-sensitive billing and reports of slower searches or constrained support. Test Free or Trial against your ingestion, query and retention requirements. Choose another product when self-hosting is mandatory or variable storage costs are unacceptable.
Our take
Sumo Logic serves organizations overseeing logs in multiple environments that want monitoring, security analytics and automation in one cloud service. API, integration and Terraform support connect existing systems. Main drawbacks are the learning curve, usage-sensitive billing and reports of slower searches or constrained support. Test Free or Trial against your ingestion, query and retention requirements. Choose another product when self-hosting is mandatory or variable storage costs are unacceptable.
- Combines logs and metrics from cloud, on-premises and hybrid environments
- Large integration catalog spanning AWS, Azure, Google Cloud and other tools
- APIs, a Python interface and Terraform provider enable automation
- Free access and a 30-day trial are offered
- Cloud SIEM and automated response capabilities
- Query language may take time to learn
- Usage and retention can drive stored-log costs upward
- Some reviewers report slower searches on large datasets
- No open-source or stated self-hosted edition
- Reviewers flag gaps in parsing and threat-intelligence coverage
- Pick it ifTeams consolidating monitoring and security data from many services; Organizations seeking cloud SIEM, dashboards and API-based automation
- Skip it ifYou require a self-hosted product edition; Your budget cannot absorb usage- and retention-based log costs; Your team needs a simple query experience with little training
Pricing
Free provides no ingestion, 7-day retention and a three-user limit. The trial runs 30 days with 1 GB per day, 30-day retention and up to 20 users. Essentials and Enterprise Suite require sales quotes.
- FreeNo ingestion · 7-day retention · Maximum 3 users · Deleted after 90 days if not upgradedFree
- Trial30 days · 1 GB/day allocation · 30-day retention · Up to 20 users · Converts to Free after trialFree
- EssentialsAnnual commitment referenced for example pricing · Ad-hoc DevOps/SecOps investigation · Dashboards and monitors · Anomaly detection · Log-to-metric correlation · Open integrationsOn request
- Enterprise SuiteContact sales · Cloud-native SIEM · MITRE ATT&CK mapping · UEBA coverage · Audit and posture monitoring · 24/7 support · Multi-organization supportOn request
As sumologic.com lists them, checked 14 Oct 2026.
Questions
Is Sumo Logic cloud-based?
Yes. The offering is described as cloud-native SaaS, with web, API, Windows, macOS and Linux access.
Does Sumo Logic have a free plan?
Yes. The Free tier has no ingestion, seven-day retention and a maximum of three users.
What is the length of Sumo Logic's trial?
Trial access runs for 30 days and includes 1 GB per day, 30-day retention and up to 20 users before moving to Free.
Does Sumo Logic offer a public API?
Yes. Its APIs support retrieval, searches, dashboards, reports, collectors, automation and Cloud SIEM operations.
Is Sumo Logic open-source software?
No. The agreement describes proprietary software, and no self-hosted edition is specified.
What does Sumo Logic integrate with?
Documented integrations include AWS, Azure, Google Cloud, Kubernetes, databases, SaaS applications and security tools.
Near it
All alternatives →- WWazuh#1 on this board
- B
 Blumira#3 on this board
- L
 LimaCharlie#4 on this board
- MDMicrosoft Defender for Business#5 on this board
- ES
 Elastic Security#6 on this board
- ML
 ManageEngine Log360#7 on this board
- H
 Hunters#8 on this board
- P
 Panther#9 on this board
- SE
 Splunk Enterprise#10 on this board
- VA
 Vectra AI Identity Threat Detection and Response#11 on this board