Vigil SIEM: Open-Source Self-Hosted Security Monitoring
vigil-siem.com · checked 15 Oct 2026
Open-source, self-hosted SIEM that evaluates Sigma detections and returns JSON for AI agents.
How it plugs in
Signal on SIEM Software7.7#2 of 29
Vigil is a free, open-source SIEM for self-hosted deployments. It collects Windows Event Logs or Linux journald, checks events against Sigma rules in real time, and supports HQL searches across event history. Commands can return JSON for AI agents, while human approval is required for destructive actions. It runs on Windows, Linux, macOS, the web, and through an API.
Review
In a line
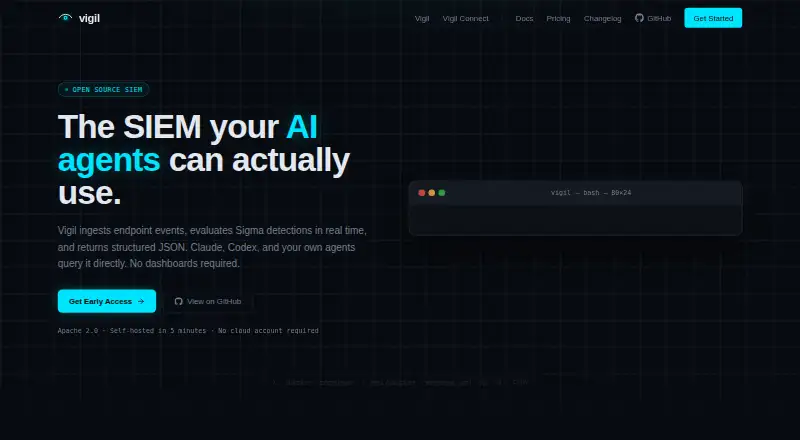
Vigil is a self-hosted, open-source security information and event management (SIEM) tool. It ingests endpoint events, evaluates Sigma detections in real time, and returns structured JSON for AI agents.
What it does
A single agent collects Windows Event Logs or Linux journald and sends batches every five seconds. Events can also arrive from any source over HTTP. Each event is checked against Sigma YAML rules before the HTTP response returns.
Vigil includes 41 Sigma rules covering 10 MITRE ATT&CK tactics. Its HQL query language searches historical events with filters, time ranges, endpoints, field values, aggregations, and timelines.
Every command can return JSON, with named playbooks for triage, investigation, hunting, and forensic sweeps. Destructive actions pause for explicit human approval; the command line waits for a response.
How it connects
Vigil is released under the Apache 2.0 license and can run without a cloud account. The local API uses port 6987 and has interactive documentation at /docs. An MCP server at /mcp exposes its security operations to external tools.
Splunk and Microsoft Sentinel connections are listed as coming soon. The wider catalogue covers areas such as cloud platforms, identity, threat intelligence, ticketing, chat, paging, and data pipelines.
The documented model stack supports Anthropic, OpenAI, Google Vertex, and local Ollama models. Claude Code can be connected with `npx @vigil/skill`, without an MCP server or a running process.
Good fit
Vigil suits teams that want to keep event data on their own systems and connect security operations to AI agents. It fits jobs such as real-time alerting, historical hunting, investigations, triage, and forensic sweeps.
Custom detection rules are supported. Secure onboarding uses short-lived enrollment tokens, and the agent is a single static binary for Windows and Linux.
Watch for
Vigil is pre-1.0. Only the latest 0.x minor release is supported, and older 0.x minors do not receive backported fixes.
Self-hosting options include Docker Compose, manual installation, Kubernetes Helm, and a desktop package. The documented prerequisites include Docker, Node.js 20 or newer, and Git; the desktop package still needs Docker installed and running.
The homepage advertises detection latency below 50 milliseconds, but the facts do not describe capacity limits or a service-level target for the free plan. Check compatibility with your existing systems before adopting it.
Pricing
The Open Source plan is free forever. It includes unlimited events, Sigma rules, HQL hunting, multiple endpoints, Windows and Linux agents, forensics, and JSON output.
The Cloud plan is coming soon, with price on request. It is listed with managed ClickHouse and PostgreSQL, automatic updates, a 99.9% uptime SLA, a web dashboard, email and Slack alerts, API keys, SSO/SAML, and dedicated infrastructure.
The Enterprise plan uses annual invoicing and is also price on request. It adds dedicated infrastructure, SSO/SAML, a custom SLA, on-premise deployment, custom detections, a dedicated Slack channel, a SOC 2 report, and custom integrations.
Verdict
Choose Vigil if you need an open-source SIEM that stays self-hosted, accepts endpoint or HTTP events, and exposes security work to AI tools through JSON and MCP. Its free plan covers the core hunting and collection features.
Avoid committing until you can manage Docker-based deployment and accept the pre-1.0 support policy. Organizations needing managed hosting, uptime commitments, or vendor support should review the Cloud and Enterprise offerings instead.
Our take
Vigil is a practical option for people who want SIEM functions without sending operations to a required cloud service. The free Open Source plan provides broad collection, hunting, detection, and JSON features, while MCP and API access support automation. Its early-stage release policy means updates require care, especially for older 0.x versions. Buyers should also plan for Docker and related setup work. Those needing managed infrastructure, formal uptime terms, or dedicated support will need a paid plan whose price is provided on request.
- Free forever Open Source plan
- Self-hosted and open source under Apache 2.0
- 41 Sigma rules across 10 MITRE ATT&CK tactics
- JSON output and MCP access for AI tools
- Windows and Linux endpoint agents
- Pre-1.0 project with limited support for older 0.x minors
- Self-hosting requires Docker-based setup
- Cloud and Enterprise pricing is on request
- Desktop package still requires Docker running
- Pick it ifTeams keeping SIEM data on their own systems; AI-assisted triage, hunting, and investigations; Users needing Windows or Linux event collection
- Skip it ifYou need a mature release with backported fixes for older versions; You want a fully managed SIEM with published pricing; You cannot run Docker or maintain self-hosted infrastructure
Pricing
The core Open Source plan is free forever. Cloud and Enterprise plans are listed as price on request; Cloud is coming soon, while Enterprise uses annual invoicing.
- Open SourceForever · Unlimited events · Sigma rules · HQL hunting · Multi-endpoint · Windows/Linux agents · Forensics · JSON outputFree
- CloudComing soon · Managed ClickHouse/Postgres · Automatic updates · 99.9% uptime SLA · Web dashboard · Email/Slack alerts · API keys · SSO/SAML · Dedicated infrastructureOn request
- EnterpriseAnnual invoicing · Dedicated infrastructure · SSO/SAML · Custom SLA · On-premise deployment · Custom detections · Dedicated Slack channel · SOC 2 report · Custom integrationsOn request
As vigil-siem.com lists them, checked 15 Oct 2026.
Questions
Is Vigil free?
Yes. Its Open Source plan is free forever and includes unlimited events, Sigma rules, HQL hunting, multi-endpoint support, agents, forensics, and JSON output.
Does Vigil require a cloud account?
No. Vigil is presented as self-hosted and can run without a cloud account.
Which systems can Vigil collect events from?
Its agent collects Windows Event Logs or Linux journald. Events can also be pushed from any source over HTTP.
What integrations are available?
The integration catalogue spans SIEM and log search, EDR/XDR, cloud platforms, identity, threat intelligence, sandboxes, ticketing, chat, paging, network security, and data pipelines. Splunk and Microsoft Sentinel are listed as coming soon.
Can AI agents use Vigil?
Yes. Commands can return structured JSON, and Vigil exposes SOC operations through an MCP server. Claude Code connects with `npx @vigil/skill`.
What does HQL do?
HQL searches the full event history using filters, aggregations, timelines, endpoint filters, time ranges, and field values.
What does Enterprise include?
Enterprise is price on request with annual invoicing. It lists dedicated infrastructure, SSO/SAML, custom SLA, on-premise deployment, custom detections, support, a SOC 2 report, and custom integrations.
Near it
All alternatives →- WWazuh#1 on this board
- U
 UTMStack#3 on this board
- SL
 Sumo Logic#4 on this board
- B
 Blumira#5 on this board
- NS
 nano SIEM#6 on this board
- MDMicrosoft Defender for Business#7 on this board
- ES
 Elastic Security#8 on this board
- MSMaxPatrol SIEM#9 on this board
- ML
 ManageEngine Log360#10 on this board
- LSLogSentinel SIEM#11 on this board